Enterprise Identity and Access Management with Microsoft Entra ID
A cloud identity environment built around least privilege, group-based access, MFA, and authentication monitoring.
The challenge
What needed to be solved
Model how a modern organization can separate privileged access, manage users centrally, strengthen authentication, and preserve evidence of identity activity.
The approach
How I worked through it
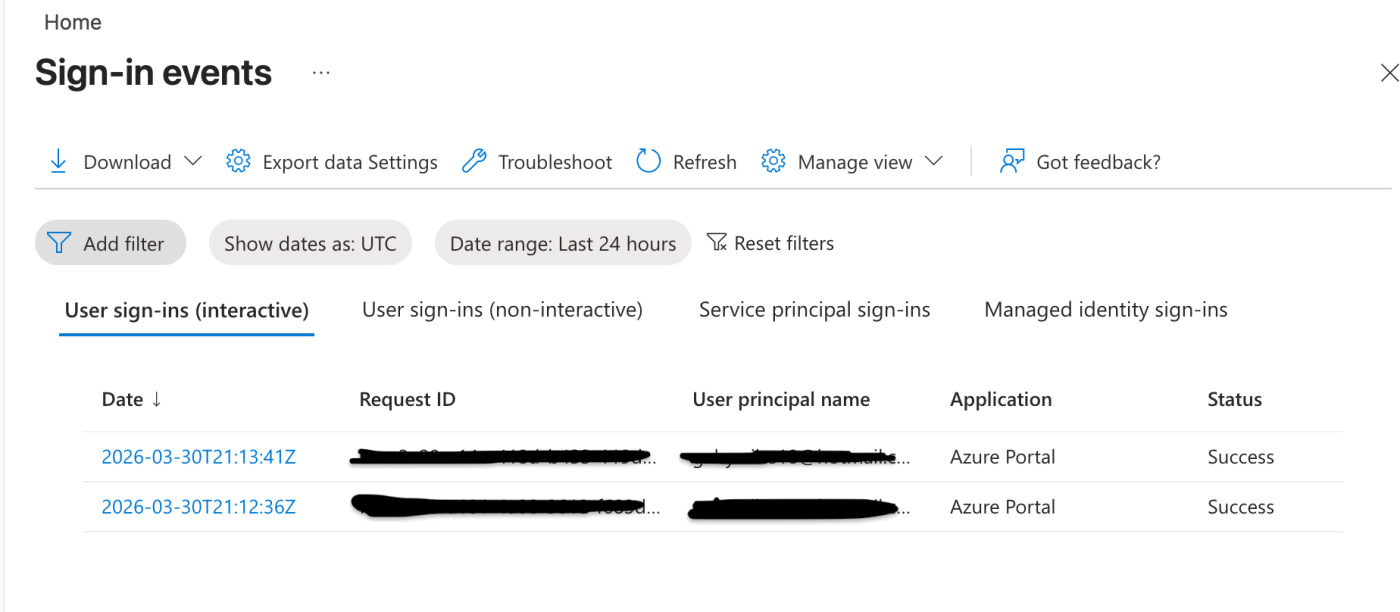
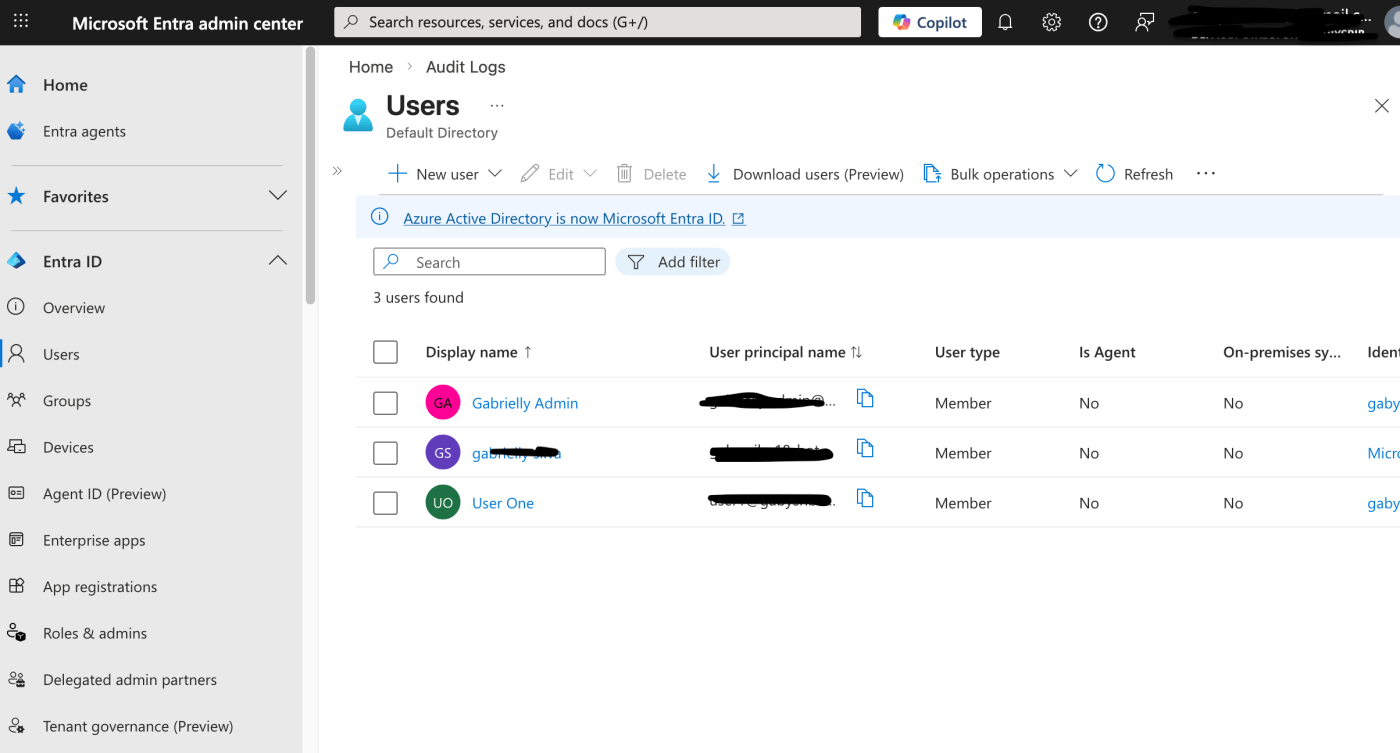
I created separate administrative and standard identities, organized access through a security group, enabled MFA, and reviewed both sign-in and audit events.
The result
What the work demonstrated
The environment demonstrated a complete identity workflow: provisioning, access assignment, stronger authentication, activity monitoring, and change auditing.
Process
From problem to validation
Separate identities
Created administrative and standard user accounts to apply least privilege and avoid unnecessary privileged activity.
Centralize access
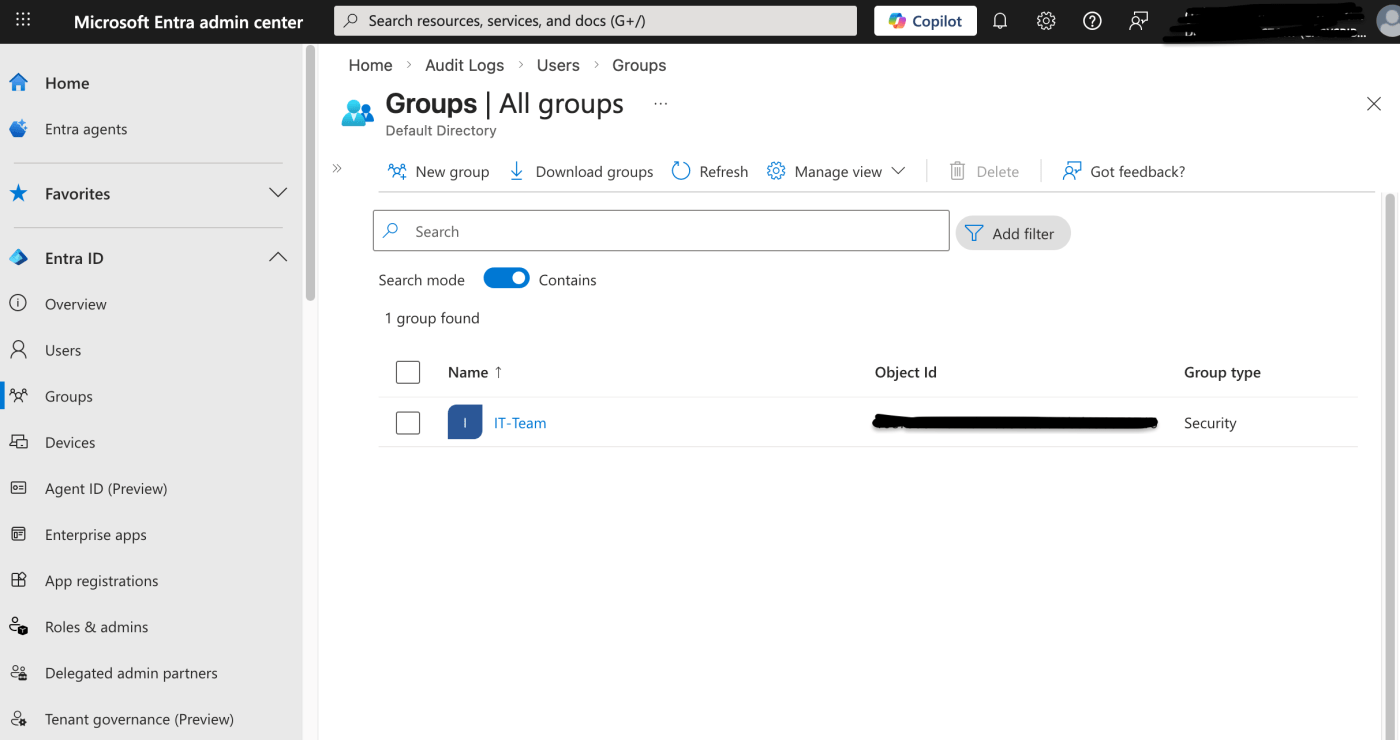
Created the IT-Team security group and assigned membership to model group-based access control.
Strengthen authentication
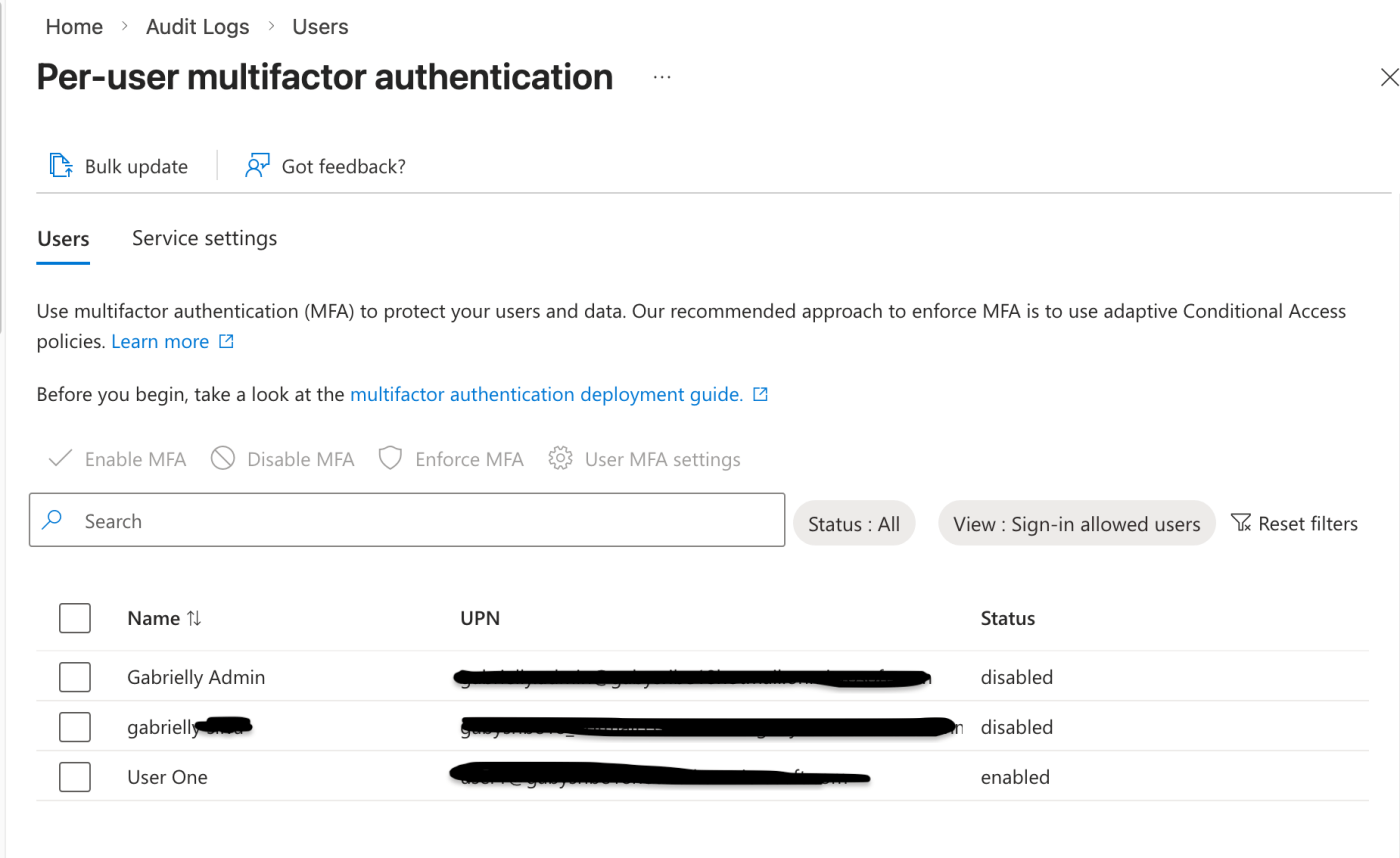
Enabled multi-factor authentication for user accounts as an additional identity protection layer.
Monitor and audit
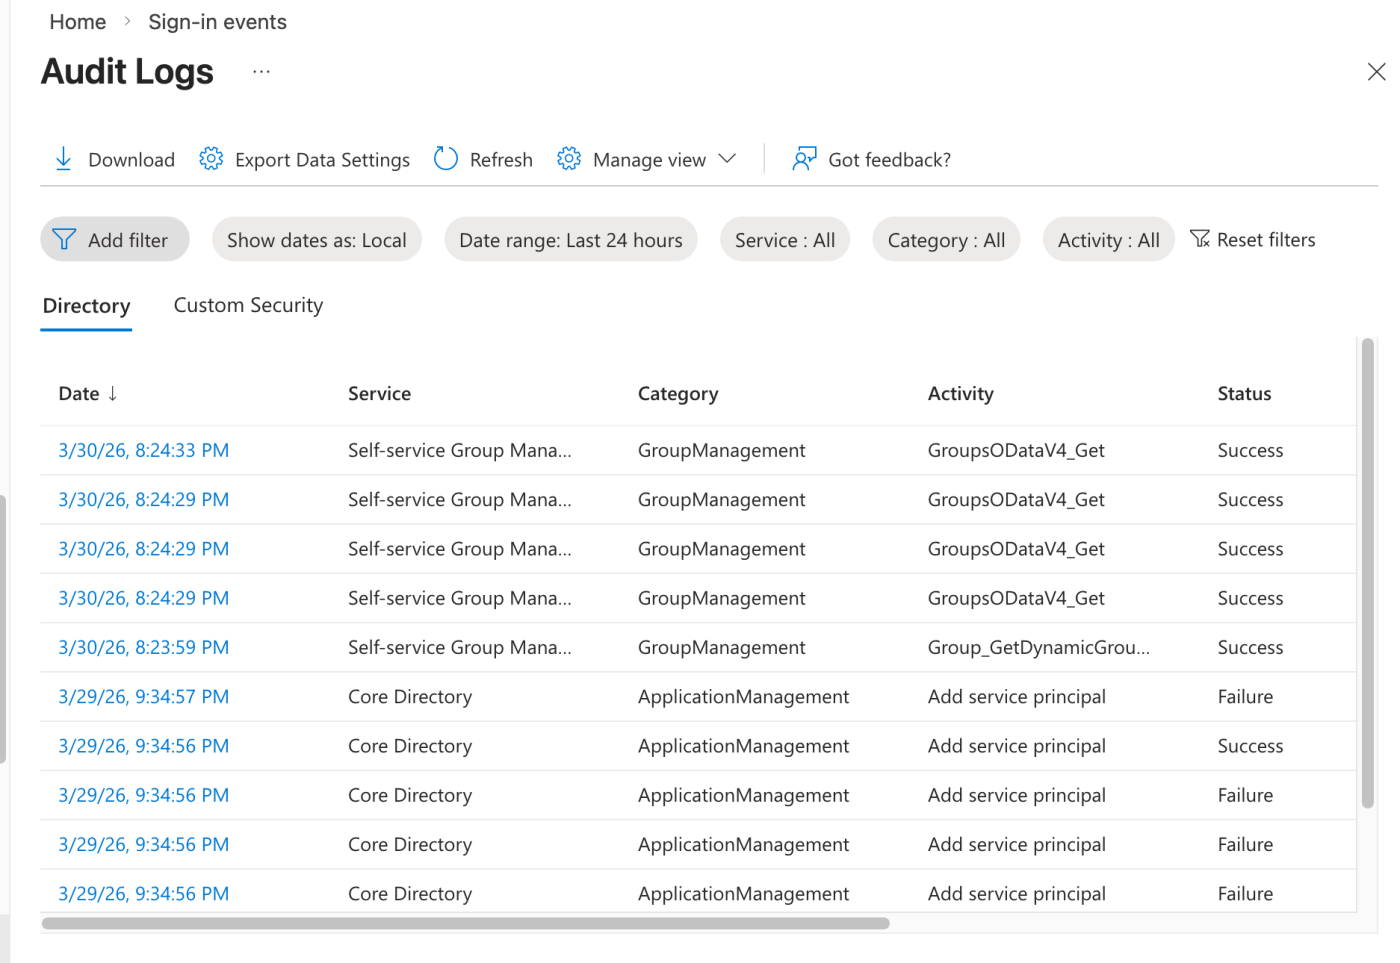
Reviewed sign-in events and audit logs to verify successful access and track user, MFA, and group changes.
Evidence
Implementation and validation
Skills demonstrated